Artificial intelligence is undergoing a profound structural evolution, shifting rapidly from passive conversational assistants and experimental proof-of-concept projects into autonomous operational agents capable of executing complex workflows across corporate networks. However, this acceleration has triggered a critical security deficit, leaving enterprise environments vulnerable to unprecedented risks. According to recent findings published in SailPoint’s Horizons of Identity Security report, an overwhelming 79% of enterprises already have AI agents actively running within production environments. Yet, in stark contrast, a mere 2% of these organizations have deployed identity security frameworks specifically engineered to govern, monitor, and regulate non-human autonomous software.
This staggering disparity between adoption velocity and security maturity has forced identity management and access governance providers to urgently rethink traditional cybersecurity paradigms. Enterprise identity security company SailPoint unveiled a suite of advanced security capabilities designed to tackle this exact dilemma at its Navigate conference. Aimed at bringing structural order to the chaotic landscape of autonomous corporate software, these offerings mark a major shift in how modern corporations plan to manage the emerging class of autonomous digital identities.
The Anatomy of the Agentic Security Gap
For decades, enterprise security architecture has been built around a fundamental, binary premise: humans log into systems, request access to specific applications, and administrators manually or programmatically approve those permissions based on corporate policy. This model, while increasingly strained by cloud computing and microservices, has remained the bedrock of organizational security.
The widespread deployment of agentic AI fundamentally shatters this assumption. Modern AI agents are no longer confined to answering questions inside a chat window; they are increasingly granted autonomous agency to access enterprise applications, ingest sensitive corporate data, manipulate backend databases, handle customer credentials, and execute multi-step transactions independently on behalf of users. When multiplied across hundreds of workflows and millions of individual tool calls, these agents effectively constitute an entirely new class of digital identity that conventional security tooling cannot adequately perceive, let alone control.
Industry experts point out that the sheer velocity of automated operations renders traditional, human-centric oversight completely obsolete. Because autonomous agents can execute thousands of programmatic operations within seconds, relying on security administrators to manually review, audit, and approve access requests creates a crippling operational bottleneck. Furthermore, the proliferation of unmonitored deployments—often referred to as "shadow AI"—compounds the threat surface, leaving IT departments blind to the full scope of autonomous software operating within their perimeters.
SailPoint’s Strategic Response: The Navigate 2026 Announcements
To bridge this dangerous operational chasm, SailPoint used its flagship Navigate conference to introduce a comprehensive expansion of its security ecosystem. The newly unveiled capabilities are strategically divided across several interconnected platforms, designed to provide end-to-end visibility, runtime authorization, and real-time mitigation against compromised or rogue AI assets.
At the core of this release is the enhancement of SailPoint’s Agentic Fabric, which now features advanced discovery mechanisms tailored specifically to unearth unmanaged "shadow AI" agents deployed by departments outside formal IT oversight. Beyond mere discovery, the upgraded fabric delivers runtime authorization controls, granting security teams the immediate capability to throttle, restrict, or entirely disable an active agent the moment anomalous or unauthorized behavior is detected.
Complementing these runtime controls is the introduction of SailPoint Autonomous Agents—a specialized category of security-focused AI agents engineered specifically to govern other autonomous software within the enterprise. Rather than relying on human intervention, these security agents continuously monitor runtime telemetry, intercept potential security threats on the fly, and dynamically adjust access permissions in real time. Crucially, they are designed to perform these interventions granularly, neutralizing malicious or erratic software threads while allowing legitimate, business-critical agents to continue operating without disruption.
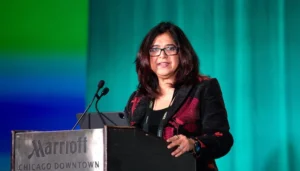
SailPoint’s executive leadership has been vocal about the necessity of this shift. Chandra Gnanasambandam, Chief Technology Officer at SailPoint, highlighted the absurdity of applying legacy administrative workflows to modern machine-speed environments during the product unveiling. "The idea that a security admin is going to review and approve access for a group of autonomous agents making 10,000 tool calls a second isn’t just outdated—it’s a fantasy," Gnanasambandam stated, emphasizing that automation must be met with equal and opposite automation.
Visibility, Posture Management, and Just-In-Time Access
Gaining control over agentic workflows requires deep foundational visibility, a challenge that SailPoint has addressed through a multi-layered telemetry collection strategy. The company’s newly introduced endpoint and browser sensors, combined with integrated Security Information and Event Management (SIEM) and Extended Detection and Response (XDR) telemetry, provide comprehensive mapping capabilities. These tools are engineered to detect undocumented agents, Model Context Protocol (MCP) servers, hidden credentials, auxiliary tools, and unauthorized data stores that have managed to bypass standard corporate onboarding pipelines.
Building upon this data aggregation layer, SailPoint also rolled out Autonomous Identity Security Posture Management (A-ISPM). Powered by identity data channeled through the company’s Atlas platform, A-ISPM continuously scans the enterprise ecosystem to flag latent vulnerabilities such as dormant service accounts, orphaned access pathways, and shadow administrators. Once risky access paths or misconfigured permissions are identified, the system empowers organizations to take immediate corrective action—whether that involves automated revocation, disabling compromised AI agents, assigning formal data owners, or enforcing compliance policies programmatically.
In tandem with posture management, SailPoint is leaning heavily into Just-In-Time (JIT) provisioning principles. Recognizing that static, permanent access grants represent a massive vulnerability when combined with autonomous software, the updated framework ensures that permissions are only granted dynamically when an authenticated entity explicitly requires them. These temporary access grants can be conditioned upon secondary reauthentication steps, automated policy checks, or documented business justifications, significantly shrinking the potential blast radius should an agent or user account be compromised.
Industry Implications and the Broader Enterprise Impact
The rollout of SailPoint’s agentic security capabilities reflects a broader, highly urgent market realization: identity is rapidly becoming the new enterprise perimeter in an AI-dominated corporate landscape. As organizations increasingly transition generative AI models from advisory copilots into core operational execution layers, securing the digital credentials and permissions of those agents is no longer an optional security enhancement—it is an existential prerequisite for digital trust.
Matt Mills, President at SailPoint, underscored the magnitude of this transition during the company’s strategic briefings. "Autonomous agents are no longer just experimental copilots; they are becoming the primary execution layer of modern enterprises," Mills observed, framing the current moment as a critical turning point for corporate risk management.
As these tools begin deploying globally—with platforms like the Agentic Fabric, Human Fabric, and Atlas rolling out progressively, and advanced features such as A-ISPM slated for release in the fourth quarter of fiscal 2027—the enterprise security sector will be closely watching adoption metrics. The core question facing chief information security officers across all major industries is whether autonomous governance frameworks can scale quickly enough to outpace the exponential growth of autonomous software development.
Ultimately, the emergence of agentic identity security signals the end of the traditional perimeter era and the dawn of automated, machine-speed defense. Organizations that successfully bridge the 79% adoption to 2% governance gap will likely harness the immense productivity gains of autonomous AI safely and securely. Conversely, those that fail to establish rigorous visibility and programmatic control over their non-human workforce may find themselves navigating an unprecedented landscape of automated security breaches, data exfiltration, and operational chaos.